Skip to content
Agent Front Desk

Security and privacy

Your data stays in your WordPress

There is no shared multi-client database and nothing is routed through us. This page lists what the product does and, below, what it does not do yet.

Data ownership

  • Conversations, leads, bookings and knowledge live in your WordPress database
  • You hold the accounts for the AI model, voice, email and CRM
  • The code is GPL and yours
  • Deactivate the plugins and your site is untouched. Uninstalling removes the tables, options and staff role.
Disclosure and consent

  • The chat opens with a notice that the visitor is talking to an AI, that it answers from your knowledge base, and that the conversation is saved
  • The disclosure wording is yours to set
  • Voice asks visitors to accept a recording notice before the microphone starts, and you word it. Rules differ by place, and checking them is your responsibility.
  • Nothing is booked until the visitor confirms

Keys and secrets

  • Keys defined in wp-config.php never touch the database
  • Keys saved in the admin are encrypted with libsodium and never shown again. Define an encryption key so a salt change cannot lock you out
  • The ElevenLabs key stays on the server. The browser only gets a one-time signed session
  • MCP tokens, authorization codes and refresh tokens are stored as hashes. A manual token is shown once
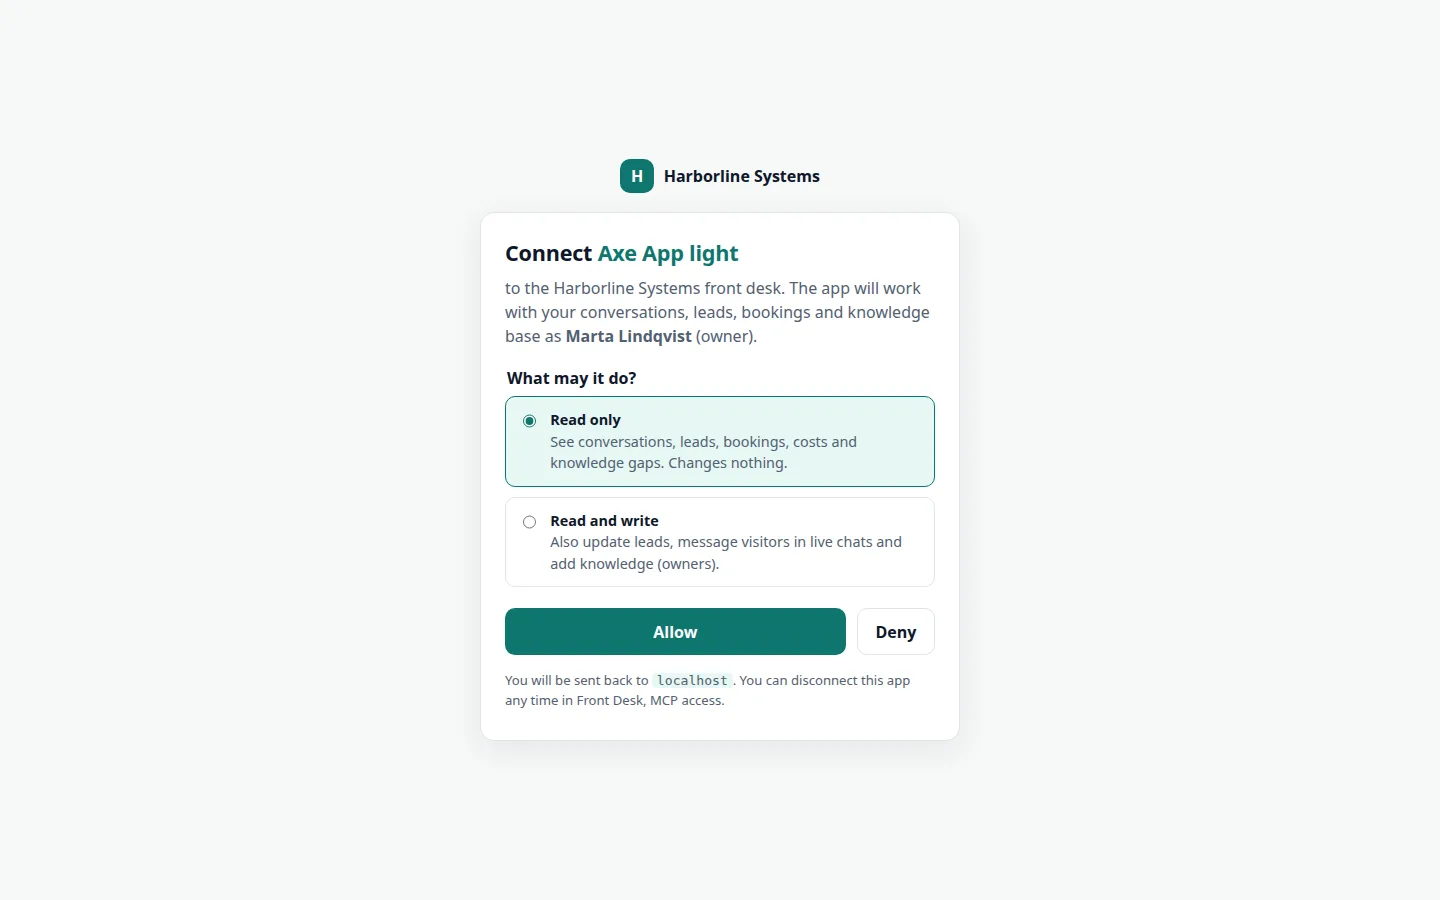
  • MCP connectors use OAuth 2.1 with PKCE, exact redirect matching, one hour access tokens and rotating refresh tokens. Reusing a refresh token revokes the grant

Who can see and do what

  • Owners are WordPress administrators. Staff have a separate Front Desk Staff capability for conversations, leads, bookings, live chats and analytics
  • Visitors are anonymous. Public routes use a signed short-lived session token and a per-conversation token, and are rate limited
  • Admin routes check capabilities and the standard WordPress nonce
  • Read-only MCP access is refused any write
  • An audit log of settings, integration, knowledge and team changes, and every MCP call and denial

What leaves your site

  • No iframes, and no third-party scripts load from the plugins. We checked the widget, the admin and a real voice call
  • The only outside services called are the ones you set up: Anthropic, ElevenLabs, HubSpot, and optional OpenAI or Voyage
  • Optional update checks happen only if you activate a license key. An unlicensed site never contacts our update server

Accessibility

  • WCAG 2.2 AA is the standard we build to, with automated axe checks on the admin screens in light and dark and on the widget
  • A keyboard and screen reader pass is done per client before launch

Limits, stated plainly

  • Chat replies stream on hosts that do not buffer PHP output. Elsewhere the widget falls back to a normal reply.
  • Rate limits are per visitor address. Put a CDN or web application firewall in front for a busy public launch.
  • Live handover covers chat, and it polls about every 2.5 seconds.
  • Live phone answering is not part of the suite yet.
  • Multisite is untested.
  • We make no certification claims such as SOC 2 or HIPAA. If you need one, we will say plainly what is and is not covered.
The connector consent screen asking for Read only or Read and write, with Allow and Deny buttons.

Have a security questionnaire?

Send it over. We answer from how the product actually works.